Connect with us
Anglostratits

Business

Kaspersky: Advanced Persistent Threat (APT41) targets Southern African organisation in espionage attack

Published

on

Kaspersky

Based on Kaspersky experts’ analysis, the attackers may have gained access to the organisation’s network through a web server exposed to the Internet

JOHANNESBURG, South Africa, July 21, 2025/APO Group/ –Kaspersky Managed Detection and Response experts (www.Kaspersky.co.za) have observed a cyber espionage attack on an organisation in Southern African and have linked it to the Chinese-speaking  APT41 group. Although the threat actor has shown limited activity in Southern Africa, this incident reveals that the cyber attackers have targeted government IT services in one of the countries in the region, attempting to steal sensitive corporate data — including credentials, internal documents, source code, and communications.

APT (Advanced Persistent Threat) is a category of threat actors known for carrying out concerted, stealthy, and ongoing attacks against specific organisations, as opposed to opportunistic, isolated incidents that account for most cybercriminal activity. The adversaries’ techniques observed during the attack in Southern Africa allowed Kaspersky to attribute it to the Chinese-speaking APT41 group with a high confidence. The primary goal of the attack was cyber espionage, which is typical for this threat actor. The attackers attempted to collect sensitive data from the machines they compromised within the organisation’s network.

It is noteworthy that APT41 typically has been showing quite limited activity in the Southern African region. APT41 specialises in cyber espionage and targets organisations across various industries, including telecommunications providers, educational and healthcare institutions, IT, energy, and other sectors, with known activity in at least 42 countries.

Based on Kaspersky experts’ analysis, the attackers may have gained access to the organisation’s network through a web server exposed to the Internet. Using a credential harvesting technique – known in professional terms as registry dumping – the attackers obtained two corporate domain accounts: one with local administrator rights on all workstations and another belonging to a backup solution, which had domain administrator privileges. These accounts allowed the attackers to compromise additional systems within the organisation.

One of the stealers used for data collection was a modified Pillager utility, designed for exporting and decrypting data. The attackers compiled its code from an executable file into a Dynamic Link Library (DLL). With it, they aimed to gather saved credentials from browsers, databases, administrative tools, as well as project source code, screenshots, active chat sessions and their data, email correspondence, lists of installed software, operating system credentials, Wi-Fi credentials, and other information.

Defending against such sophisticated attacks is impossible without comprehensive expertise and continuous monitoring of the entire infrastructure

The second stealer used during the attack was Checkout. In addition to saved credentials and browser history, it was also capable of collecting information on downloaded files and browser-stored credit card data. The attackers also used the RawCopy utility and a version of Mimikatz compiled as a Dynamic Link Library (DLL) to dump registry files and credentials, as well as Cobalt Strike for Command and Control (C2) communication on compromised hosts.

“Interestingly, as one of their C2 communication channels besides Cobalt Strike, the attackers chose the SharePoint server within the victim’s infrastructure. They communicated with it using custom C2 agents connected with a web-shell. They may have chosen SharePoint because it was an internal service already present in the infrastructure and unlikely to raise suspicion. Moreover, in that case, it probably offered the most convenient way to exfiltrate data and control compromised hosts through a legitimate communication channel,” explains Denis Kulik, Lead SOC Analyst at Kaspersky Managed Detection and Response service.

“In general, defending against such sophisticated attacks is impossible without comprehensive expertise and continuous monitoring of the entire infrastructure. It is essential to maintain full security coverage across all systems with solutions capable of automatically blocking malicious activity at an early stage — and to avoid granting user accounts excessive privileges,” comments Denis Kulik.

To mitigate or prevent similar attacks, organisations are advised to follow these best practices:

  • Ensure that security agents are deployed on all workstations within the organisation without exception, to enable timely incident detection and minimise potential damage.
  • Review and control service and user account privileges, avoiding excessive rights assignments – especially for accounts used across multiple hosts within the infrastructure.
  • To protect the company against a wide range of threats, use solutions from the Kaspersky Next (https://apo-opa.co/44EI2e3) product line that provide real-time protection, threat visibility, investigation and the response capabilities of EDR and XDR for organisations of any size and industry. Depending on your current needs and available resources, you can choose the most relevant product tier and easily migrate to another one if your cybersecurity requirements are changing.
  • Adopt managed security services by Kaspersky such as Compromise Assessment (https://apo-opa.co/4m8aElL), Managed Detection and Response (MDR) (https://apo-opa.co/4m6do37) and / or Incident Response (https://apo-opa.co/44VsAsP), covering the entire incident management cycle – from threat identification to continuous protection and remediation.  They help to protect against evasive cyberattacks, investigate incidents and get additional expertise even if a company lacks cybersecurity workers.
  • Provide your InfoSec professionals with an in-depth visibility into cyberthreats targeting your organisation. The latest Kaspersky Threat Intelligence (https://apo-opa.co/3TQbRlK) will provide them with rich and meaningful context across the entire incident management cycle and helps them identify cyber risks in a timely manner.

A detailed analysis of the incident is available on Securelist (https://apo-opa.co/46mfGGS).

Kaspersky Managed Detection and Response service monitors suspicious activity and helps organisations respond swiftly to minimise impact. This is a part of Kaspersky Security Services, a team delivering hundreds of information security projects every year for Fortune Global 500 organisations: incident response, managed detection, SOC consulting, red teaming, penetration testing, application security, digital risks protection.
Distributed by APO Group on behalf of Kaspersky.

Home  Facebook

Business

SLB commissions new fluids systems plant in Pemba to support Mozambique’s offshore energy development

Published

on

Mozambique

New facility expands in-country drilling and completion fluids capability, advancing the next phase of SLB’s growth in Mozambique

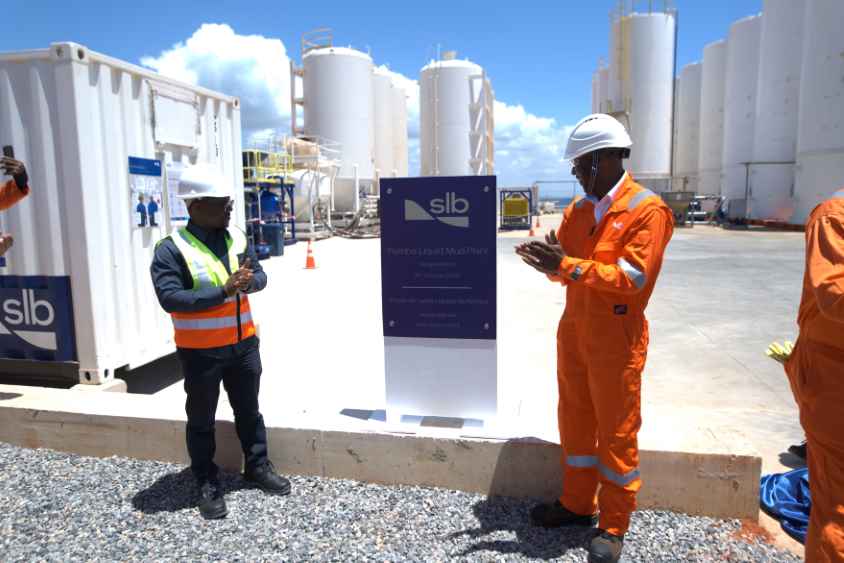
PEMBA, Mozambique, October 9, 2026/APO Group/ –SLB (NYSE: SLB) (www.SLB.com) announced the opening of a new fluids systems plant in Pemba, Mozambique. The new facility strengthens in-country capacity to prepare, store and deliver drilling and completion fluids for offshore operations, reinforcing the infrastructure needed as Mozambique’s offshore activity grows and its role as a strategic energy hub for East Africa continues to expand.

The commissioning of the plant, also known as a liquid mud plant, coincides with SLB marking 70 years of operations in Mozambique. It reflects the company’s long-term commitment to investing in people, infrastructure and capability that support the country’s long-term offshore energy development plans.


With an initial storage capacity of 21,000 barrels, the liquid mud plant provides a scalable platform for future growth, supporting multiple customers and rising offshore activity while improving logistics and enhancing operational flexibility.

As SLB marks 70 years in Mozambique, this investment reflects our confidence in the country’s future and our commitment to supporting its energy ambitions

“As SLB marks 70 years in Mozambique, this investment reflects our confidence in the country’s future and our commitment to supporting its energy ambitions,” said Miguel Baptista, Central, East and Southern Africa, Managing Director, SLB. The new liquid mud plant strengthens local energy infrastructure, expands opportunities for local content development, and enhances our ability to support customers as they deliver some of Africa’s most significant offshore energy resources.”

The liquid mud plant project was delivered with strong local participation and that momentum is expected to continue into operations. During project delivery, more than 100 jobs were created in Pemba with nationals representing 80% of the workforce, reflecting a focus on building local capability.

The project was delivered with a strong focus on safety, operational integrity, and quality, achieving more than 67,000 hours worked without a recordable safety incident.

This key infrastructure strengthens SLB’s ability to support consistent service quality and enhance supply chain readiness for increasing offshore activity across Mozambique, supporting customers execute safely and efficiently while developing local skills and expertise.

Key Points:

  • SLB has commissioned a new fluids system plant in Pemba, expanding in-country drilling and completion fluids capability for offshore operations.
  • With an initial storage capacity of 21,000 barrels, the facility provides a scalable platform to support growing offshore activity in Mozambique.
  • The investment marks the next phase of SLB’s growth in Mozambique, strengthening local capability and supporting long-term offshore energy development.

Distributed by APO Group on behalf of SLB.


Continue Reading

Business

South African Energy Storage Association (SAESA) welcomes 4,600 MW battery storage prioritisation and calls for integrated energy planning

Published

on

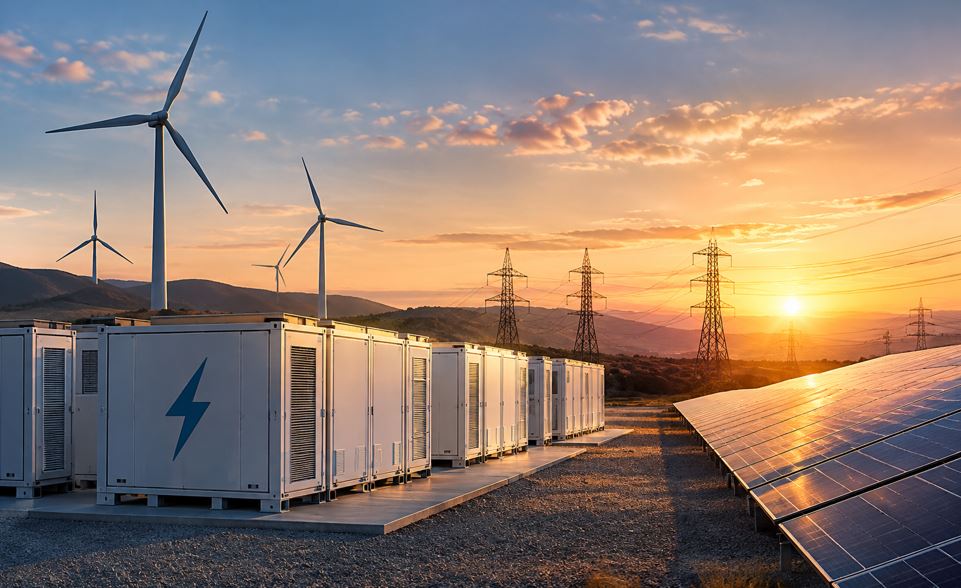
Battery energy storage systems (BESS) are becoming critical system infrastructure, supporting flexibility, reducing avoidable curtailment, shifting energy into periods of demand and strengthening security of supply

JOHANNESBURG, South Africa, October 9, 2026/APO Group/ –The South African Energy Storage Association (SAESA) (www.SAESA.org.za) welcomes the prioritisation of 4,600 MW of battery energy storage under the first Integrated Resource Plan (IRP) 2025 Section 34 determination.


The timing is significant. Recent Integrated Energy Plan (IEP) modelling and assumptions discussions highlighted a fundamental shift that South Africa’s energy planning now needs to capture: we cannot plan the future power system by counting megawatts of generation alone.

We must plan for when energy is available, where it is available, how it moves through a constrained grid and how it is stored and dispatched when the system needs it most.

The announcement reinforces that shift. Battery energy storage systems (BESS) are becoming critical system infrastructure, supporting flexibility, reducing avoidable curtailment, shifting energy into periods of demand and strengthening security of supply.

For SAESA, the message for the IEP is clear: storage, flexibility and system services must be modelled as integral components of South Africa’s future electricity architecture, with their contribution considered from the outset of generation planning.

“The IEP must plan the power system we are becoming, not simply model the power system we have inherited,” says SAESA.

The IEP must plan the power system we are becoming, not simply model the power system we have inherited

Partnership with C&I Energy + Storage Summit

SAESA is an association partner of the C&I Energy + Storage Summit, created by VUKA Group, taking place on 28–29 October 2026 at The Maslow Hotel, Sandton, Johannesburg.

The summit brings together commercial and industrial energy users, project developers, financiers, regulators and solution providers to explore practical approaches to energy security, procurement and storage deployment.

For businesses assessing how storage can support their operations, the event offers an opportunity to meet SAESA and engage with the wider energy community on the decisions shaping South Africa’s evolving electricity system.

Commercial and industrial energy decision-makers are invited to apply to attend as hosted buyers. Qualifying buyers receive complimentary summit access and curated opportunities to engage with industry partners.


Meet SAESA at C&I Energy + Storage Summit: Join the Hosted Buyer Programme

The Hosted Buyer Programme connects commercial and industrial energy decision-makers with solution providers shaping South Africa’s evolving private energy market.

Qualified energy buyers receive complimentary access to the summit and curated engagement with industry partners exploring energy procurement, storage deployment and project development.

Apply for the Hosted Buyer Programme (https://apo-opa.co/4ehLijJ)

Distributed by APO Group on behalf of VUKA Group.


Continue Reading

Business

Afreximbank welcomes launch of Africa Credit Rating Agency as an important step in strengthening Africa’s financial architecture

Published

on

Expanding credible rating coverage can improve the information available to investors and support the development of deeper domestic and regional capital markets

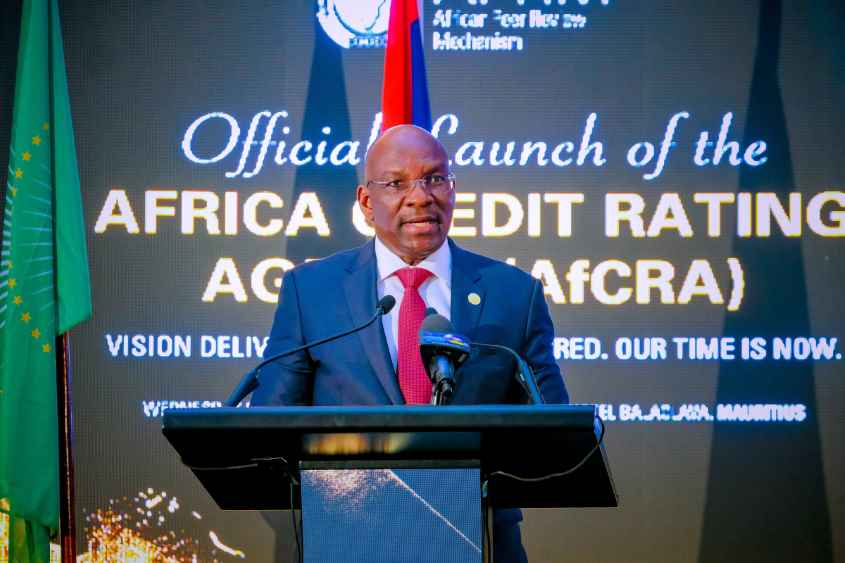
PORT LOUIS, Mauritius, October 8, 2026/APO Group/ –African Export-Import Bank (Afreximbank) (www.Afreximbank.com) welcomes today’s launch of the Africa Credit Rating Agency (AfCRA), an important milestone in strengthening Africa’s financial architecture and expanding the continent’s capacity to generate credible, independent analysis of African credit risk.


Credit ratings play an important role in determining access to capital, influencing investor perceptions and shaping the cost at which governments, institutions and businesses can finance development. It is therefore essential that assessments of African credit risk are independent, rigorous and evidence-based, while reflecting a complete understanding of the structures, institutions and economic realities being assessed.

The establishment of AfCRA adds an important African-led source of credit opinion to the market. Its value will not be measured by whether it produces more favourable ratings, but by the credibility of its analysis, the quality of its data and transparency of its methodology, and its ability to deepen understanding of African sovereigns, sub-sovereigns and corporate credit.

This is particularly important given that many African issuers remain unrated, while local-currency and sub-sovereign markets continue to have limited rating coverage. Expanding credible rating coverage can improve the information available to investors and support the development of deeper domestic and regional capital markets.

AfCRA must set a new benchmark for the continent, maintain its independence, and remain wholly owned and controlled by Africans

Alongside fellow members of the Alliance of African Multilateral Financial Institutions (AAMFI), Afreximbank has consistently maintained that African Multilateral Financial Institutions should be assessed on the basis of their fundamentals, performance, legal frameworks, mandates and operating models. Ensuring that these institutional characteristics are properly understood is essential to achieving informed, balanced and credible assessments of African risk.

Commenting on the uniqueness of the African market, and need for AfCRA’s rating methodology to reflect this, Mr Denys Denya, Senior Executive Vice President, Afreximbank, said: “The rating methodology AfCRA develops must recognise the uniqueness of our environment and its institutional structures. The Agency must set its own standards and not follow those set elsewhere — it must build a unique identity that conforms to an ‘African best practice.”

Highlighting the need for the autonomy of the Africa Credit Rating agency as it takes off, Mr Denya added: “Most importantly, AfCRA must set a new benchmark for the continent, maintain its independence, and remain wholly owned and controlled by Africans. We must all use it, and in return expect a complete assessment of where we (Africa) stand: the strengths the market has ignored, and the weaknesses we still need to fix.”

AfCRA should therefore be seen as complementary to existing international and regional rating agencies, broadening the range of credible analysis available to investors and issuers while strengthening competition, transparency and analytical capacity within Africa’s credit markets.

As Africa seeks to mobilise the scale of capital required for industrialisation, trade, infrastructure and economic transformation, credible African institutions that improve information, strengthen market confidence and deepen the continent’s financial markets will become increasingly important.

Afreximbank congratulates the African Union, the African Peer Review Mechanism (APRM) and all those involved in bringing AfCRA from concept to launch, and looks forward to the contribution the Agency will make to deeper, more transparent and more efficient African capital markets.

Distributed by APO Group on behalf of Afreximbank.


Continue Reading

Trending