Connect with us
Anglostratits

Business

How do we Build Powerful Defense with Data Storage (By Ning Yun)

Published

on

Data Storage

A Cybereason report shows that 49% of enterprises who pay the ransom either get only part of their data back, or none at all

JOHANNESBURG, South Africa, October 21, 2022/APO Group/ — 

By Ning Yun, Director of Data Storage Department of Huawei SAR (Huawei.com) 

Ransomware is striking at an alarming rate. Information technology research and consultancy company Gartner predicts, by 2025, at least 75% of IT organizations will face one or more attacks. Refined hacking tools and extortion strategies have made ransomware the biggest threat to individual, enterprise, and national data security.

Constant ransomware attacks cause huge damage

When ransomware strikes, it steals and encrypts valuable data. Encrypted data can be decrypted only by paying the hackers a ransom. Hackers, working through darknets, usually demand Bitcoin to make the payment as difficult as possible to trace. The damage ransomware creates is great, as are hackers’ profits.

According to leading investment consulting firm Cybersecurity Ventures, by 2031, ransomware is expected to attack a business, consumer, or device every 2 seconds. In 2021, this number was only 11 seconds. Even at that lower frequency, that same year, global ransomware damages reached US$20 billion — 61 times more than in 2015 (US$325 million). The largest ransom — so far — was US$70 million. But do ransoms solve the problem? No. A Cybereason report shows that 49% of enterprises who pay the ransom either get only part of their data back, or none at all. 80% of enterprises who pay the ransom are targeted a second time. Ransoms are also not the only problem: ransomware damages brands, causes long service interruptions, exposes enterprises to legal liability, and more. Such collateral damage can be enormous: as much as 23 times the ransom.

  • In March 2021, hackers encrypted 15,000 devices belonging to an insurance corporation. Vast numbers of customer data files were at risk of being leaked. The company paid US$40 million to retrieve the data.
  • In May 2021, ransomware halted all the operations of an oil pipeline giant for 11 days. Gasoline prices in the country rose to their highest level in seven years, leading to panic buying. The company paid a ransom of US$4.4 million.
  • In April 2022, a leading car manufacturer had to cut its annual production by 500,000 vehicles following an attack on its suppliers which resulted in a 1.4 TB data leak.
  • In May 2022, two attack waves caused a country to declare a cyber security emergency. They damaged basic services like healthcare, and even international trade.

There are many more examples. Hackers target large, high-value enterprises and industries. Government, energy, transportation, finance, manufacturing, and healthcare are their main objectives, but no one is safe.

Ransomware trends to know

Ransomware is extremely good at disguise. It has many ways to get into your system, for example storage, phishing emails, Trojans, social networks, and malicious insiders. It is difficult to detect and defend against. A typical attack encrypts or deletes all local data copies and can even target disaster recovery (DR) centers, making it impossible to quickly restore data. What follows, according to a ZDNet report, is an average of 16 business days system downtime. The average cost to recover from an attack, calculated by Sophos, is US$1.85 million.

There are four important ransomware trends:

Hackers focus on large enterprises and infrastructure

Instead of launching broad campaigns, ransomware attacks now increasingly focus on high-value targets. The research that hackers need to do for this approach to work is difficult, time-consuming — weeks or even months! — and expensive, but the potential profits make it worthwhile. Elaborate attacks make even previously well protected organizations potential victims, and also threaten government departments.

  • Ransomware as a Service (RaaS)

Rapid development of network and information technologies as well as encrypted digital currencies has created a hotbed for malicious actors. Ransomware operators now sell ransomware-related services to other attackers through customized solutions, memberships, or subscriptions. This lowers the barrier to entry for launching ransomware attacks, resulting in explosive ransomware growth.

Double extortion becoming the new normal

Ransomware is not limited to encrypting data and demanding ransoms. Attackers also steal data, and threaten to leak it. Even if an enterprise has a recent backup, it still cannot risk a leak of confidential information and subsequent public scrutiny and compliance proceedings.

A typical attack encrypts or deletes all local data copies and can even target disaster recovery (DR) centers, making it impossible to quickly restore data

APT-like attack capabilities

Advanced Persistent Threat (APT) refers to a complex continuous network attack customized by expert attackers to take full advantage of a victim’s vulnerabilities. Ransomware attacks, featuring greater and greater precision and planning, are beginning to show a strong resemblance to APT attacks.

Data security needs

Complex ransomware poses a great challenge for many current defense measures. Traditional data security protection focuses on the network (such as the firewall and security gateways) and on hosts to prevent ransomware intrusions and limit spread. This, however, neglects ransomware’s ability to disguise itself and lurk in the system for a long time in order to get access permissions to a large volume of key data. In other words, once the system is infected, traditional data security protection is useless. A better solution is needed.

The Defense-in-Depth framework developed by defense contractor Northrop Grumman provides good ideas on how to move forward and build stronger protection. This approach to cybersecurity features five defensive mechanism layers: perimeter, network, endpoint, application, and data security.

  • Perimeter and network security protection, established at the network layer, defends using firewalls, sandboxes, and situation awareness.
  • Endpoint and application security protection, established at the host layer, defends using access control, security patches and audits, and antivirus software.

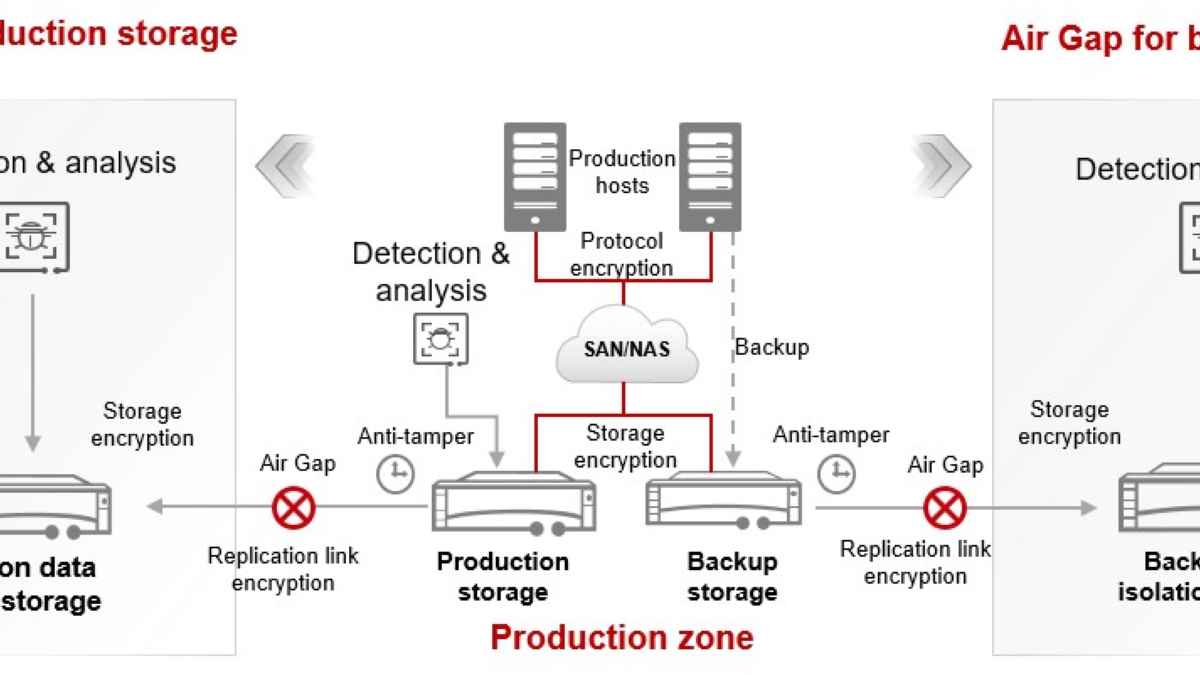
The last layer, data security, is where data storage comes in. In the modern, digital age, data storage needs to do more than just store data. It needs to serve as the last line of defense: protect data with anti-tamper technologies, detect abnormal I/Os generated by ransomware, and prevent data leaks using encryption technologies. In addition to all this, it needs to ensure it is possible to recover clean, uninfected data by keeping data copies in backup storage and in a physically isolated zone.

Building powerful ransomware defense with professional storage

Providing dual protection with production and backup storage, Huawei ransomware protection storage solution uses four key technologies to build a complete solution which prevents viruses from hiding and stealing or tampering with data: ransomware detection, data anti-tampering, air gap replication, and end-to-end data encryption. Let’s take a look at why dual protection and the four key features are so effective:

  • Dual ransomware protection with both primary and backup storage

In this solution, both primary and backup (OceanProtect Backup Storage) storage provide all-round ransomware protection features, ensuring the system always has a clean data copy for quick service recovery. OceanProtect Backup Storage also provides an ultra-fast recovery speed: up to 172 TB/hour, five times faster than the benchmark in the industry. This helps enterprises slash service downtime and economic losses.

  • Four key technologies for comprehensive protection

Ransomware detection (ransomware has nowhere to hide): Huawei ransomware detection and analysis feature delivers 99.9% accuracy for production and backup storage before, during, and after attacks. Before an attack, the storage works to intercept ransomware before it has a chance to strike. If an attack does still occur, the storage acts quickly to secure the system, working with security devices such as firewalls to isolate hosts that send abnormal I/Os, preventing ransomware from spreading to other hosts. After the attack, the storage examines data copies to ensure they are clean.

Data tampering prevention (data cannot be modified): WORM file system and secure snapshot technology block file tampering. The WORM system supports setting a protection period, preventing modification or deletion of production or backup data for the duration of the period. Read-only secure snapshots provide similar protection: they do not allow deletion or modification of data during a configured protection period.

Physical isolation (clean data copies are physically isolated): Air-gap technology enables storing a clean copy of production and backup storage data in a physically isolated zone. Even if — unlikely though it may be — both production and backup storage are compromised, the isolation zone will have a clean copy that can be used to quickly restore services. Setting the replication Service Level Agreement (SLA) will automatically replicate periodic data copies from the production or backup storage to the isolation environment. Since the replication link is active only during replication, the possibility of ransomware accessing data in the isolation zone is relatively low. For added security, the isolation zone storage also features multi-layer data protection, supporting anti-tamper features such as secure snapshots.

End-to-end encryption (data will not be leaked): Huawei storage ensures zero data leaks on the storage transmission network and storage through encryption of: protocol, production and backup storage, air-gap replication link, and remote replication transmission of data and backup copies. Even if hackers break the storage or intrude the storage network, they have no access to the confidential data thanks to the encryption deployment.

End-to-end encryption (data will not be leaked): Huawei storage uses end-to-end encryption technology to ensure no data leaks either on storage devices or on the storage transmission network. The encryption covers protocol, production and backup data, the air-gap replication link, and remote data replication. Even if hackers manage to enter a system, they will not crack confidential data.

Defending against ransomware

Huawei’s ransomware protection storage solution is working 24/7 around the world for large customers in energy, finance, transportation, manufacturing, and government.

Better safe than sorry. Installing ransomware protection after the fact is too late. A comprehensive ransomware protection storage solution is the best way to stop or mitigate ransomware.

For more information about how you can build powerful defense for your data, visit our website (https://bit.ly/3RRI74g).

Distributed by APO Group on behalf of Huawei Enterprise.
Business

Afreximbank Announces Speakers for Africa’s Largest Compliance Forum

Published

on

Afreximbank

Bankers, compliance specialists and fintech leaders from more than 40 countries will explore how regulatory cooperation and technology can align compliance approaches, reduce barriers and advance intra-African and global trade

CAIRO, Egypt, November 3, 2026/APO Group/ –Afreximbank (www.Afreximbank.com) has announced speakers for its 2026 Compliance Forum, Africa’s largest compliance-focused gathering. Discussions will address regulatory fragmentation and barriers across Africa, improve access to correspondent banking services, and explore how technology can strengthen compliance and facilitate cross-border trade


Organised in partnership with the Botswana Investment and Trade Centre (BITC), the Forum will take place from 16 to 18 November 2026 at the Gaborone International Convention Centre in Botswana. Discussions will focus on strengthening regulatory cooperation, improving access to financial services and using technology to support effective compliance across African markets.

Confirmed speakers include Governor Lesego Caster Moseki, Bank of Botswana, Dr. Patrick Ndzana Olomo, Ag. Director, Economic Development, Integration and Trade, and Head of Economic Policy and Sustainable Development, African Union Commission (AUC), Luis Koberg, Founder and CEO of Klearium Group; Shane Ridel, CEO of Elucidate, Sophie Barre, Global Head of Risk and Compliance at Wave Mobile Money Group; Mr Mooketsi Ramanteba, Non-Bank Financial Institutions Regulatory Authority (NBFIRA), Nellie Nuyoni, Head of Private Sector, CBZ Holdings, Moira Mapundu, Head of Compliance, NMB Bank Limited and Boitumelo William of Continental Reinsurance. Compliance specialists from Dow Jones and Standard Chartered will also participate.

Mr Keletsositse Olebile, Chief Executive Officer of the Botswana Investment and Trade Centre, said: “Strong and predictable compliance systems build investor confidence, protect institutions, and create the conditions in which trade and enterprise can flourish.”

Under the theme “Better Compliance – Better Trade: Leveraging Compliance to Promote African Regulations that Advance Intra-African Economic and Trade Integration,” the Forum will examine how African markets can make their regulatory systems work more effectively together while preserving national sovereignty.

Idrissa Diop, Compliance Director at Afreximbank, said: “Our banks across Africa operate across very different legal systems, supervisory approaches and levels of digital maturity. Africa does not need uniformity at any cost. It needs interoperability that reduces friction while preserving regulatory sovereignty.

Our banks across Africa operate across very different legal systems, supervisory approaches and levels of digital maturity

“We invite regulators, compliance specialists, banks, fintechs, trade institutions and technology providers from across the continent to come to Gaborone ready to turn shared principles into practical cooperation, because better compliance can and should deliver better trade for Africa.”

The opening session, “Is Better Compliance Leading to Better Trade?”, will assess how regulatory cooperation can facilitate cross-border business. Other sessions will cover anti-money laundering and countering the financing of terrorism, sanctions, cybersecurity, consumer protection and the use of artificial intelligence in compliance.

Access to correspondent banking services will be a key focus. Luis Koberg, Founder and CEO of Klearium Group, said: “Many African banks continue to face barriers to accessing correspondent banking services. The reasons given often overlook a fundamental challenge: limited visibility across the payment chain. Improved transparency gives our industry the ability to accurately assess and manage risk, on a case-by-case basis with confidence.”

Delegates will also examine how fintech and risk-based onboarding can extend access to affordable financial services while meeting compliance requirements.

Sophie Barre, Global Head of Risk and Compliance at Wave Mobile Money Group, said: “Fintechs are rewriting the rules of financial inclusion and efficiency. By combining world-class technology with intelligent, risk-based onboarding, they can deliver affordable, simple and reliable services within a compliant ecosystem.”

The Compliance Forum will also feature an exhibition of AI-enabled anti-money laundering and counter-terrorist financing compliance systems. These demonstrations will let delegates engage with emerging technologies that can strengthen risk detection, monitoring, and reporting.

This Forum comes as artificial intelligence, automation, cybersecurity, third-party risk and diverging regulatory requirements place new demands on financial institutions. These developments reinforce the need for compliance approaches that reflect Africa’s regulatory, economic and institutional realities while drawing on global good practices.

ACF2026 will provide a platform for stakeholders to redefine compliance strategies for a changing financial environment and develop practical approaches that protect institutions while enabling more efficient movement of capital, goods and services across African borders.

For programme details and registration, visit ACF2026 (https://apo-opa.co/4iVtopG)

Distributed by APO Group on behalf of Afreximbank.


Continue Reading

Business

Gas Exporting Countries Forum (GECF) Leadership Roundtable Brings Gas Producer Coordination to Paris

Published

on

Etu Energias

As African gas producers navigate rising domestic demand, global LNG competition and a renewed push for investment, the GECF Leadership Roundtable at the Invest in African Energy 2027 Forum will examine how greater coordination can support project development, market access and long-term gas monetization

PARIS, France, November 3, 2026/APO Group/ –Africa’s gas industry is entering a period in which cooperation between producing countries could become increasingly important. Demand is rising, LNG markets are being reshaped by geopolitical disruptions and new supply, while major gas developments across the continent continue to compete for capital.


Against this backdrop, the GECF Leadership Roundtable at the Invest in African Energy (IAE) Forum 2027 in Paris will bring the perspectives of gas-producing countries into a discussion focused on the commercial and strategic priorities shaping the sector.

The session comes as Africa continues to expand its role in global LNG markets. The GECF forecasts LNG exports from the continent to reach about 110 billion cubic meters (bcm), or 80 million tons per annum (mtpa), by 2030, rising to 215 bcm, or 160 mtpa, by 2050. The outlook spans producers including Algeria, Angola, Egypt, Equatorial Guinea, Mozambique, Mauritania, Senegal and Nigeria, while GECF projections point to growing LNG trade with Asia and within African markets.

Recent developments have reinforced the strategic value of that supply base. Tanzania’s long-delayed $42 billion LNG project has gained renewed attention as disruptions to Middle Eastern gas supplies have increased the value of diversified LNG sources, while ExxonMobil is advancing preparations for Mozambique’s Rovuma LNG project after years of delay.

For African producers, however, expanding exports is only one part of the equation. Domestic gas demand is rising at the same time that governments are seeking to use gas to improve electricity supply, support industrial development and create new revenue streams. That creates a need to balance export projects with domestic offtake, pipeline infrastructure, gas processing and gas-to-power development.

Coordination between producing countries can help address some of these challenges. Sharing experience on fiscal frameworks, project development, infrastructure and market access can help governments compete for investment while strengthening the case for regional gas infrastructure and cross-border trade.

The global market is also becoming more competitive. Reuters reported this month that gas and LNG infrastructure investment is expanding across multiple regions, with Asia accounting for the largest share of planned LNG import capacity. At the same time, disruptions to Middle Eastern supply have reinforced concerns around security of supply and increased the strategic importance of alternative producers. That creates an opening for African gas producers, but converting that opportunity into projects will require capital, infrastructure and credible long-term markets.

The GECF Leadership Roundtable at IAE 2027, taking place in Paris from May 11-13, will provide a senior-level setting to examine those issues alongside the investors and project developers needed to advance them. The wider forum is designed to connect African energy markets with global capital, with a focus on projects spanning gas, LNG, infrastructure and power.

For African gas producers, the question is how effectively its resources can be developed, connected to markets and converted into reliable energy and industrial growth. The Paris roundtable will put producer coordination at the center of that investment conversation.

Distributed by APO Group on behalf of Energy Capital & Power.


Continue Reading

Business

Islamic Corporation for the Development of the Private Sector (ICD) and Open Bank Sign Expression of Intent for a Potential USD 10 Million Line of Financing in Uzbekistan

Published

on

Islamic Corporation

The EoI sets out the intent to establish a Shariah-compliant LoF facility of up to USD 10 million from ICD to Open Bank to be deployed for the onward financing of eligible private sector projects, including small and medium-sized enterprises (SMEs) and corporates operating in the Republic of Uzbekistan

JEDDAH, Saudi Arabia, November 1, 2026/APO Group/ –

  • ICD and JSC Open Bank (Uzbekistan) have signed an Expression of Intent for a potential Shariah-compliant Line of Financing facility of up to USD 10 million
  • The facility aims to channel funds to eligible private sector projects, including SMEs and corporates across Uzbekistan
  • The potential Line of Financing facility intends to support job creation and SME growth, contributing to broader economic development in Uzbekistan
  • Open Bank, a privately owned digital bank licensed by the Central Bank of Uzbekistan, will serve as the intermediary institution to channel the funds to private enterprises


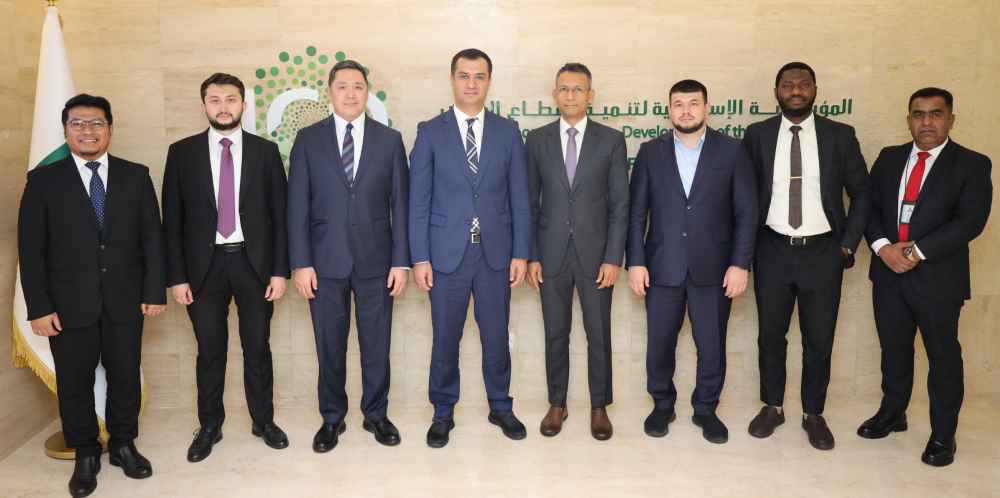
The Islamic Corporation for the Development of the Private Sector (ICD) (www.ICD-PS.org), the private sector arm of the Islamic Development Bank (IsDB) Group, and Joint Stock Company “Open Bank” (Open Bank) from Uzbekistan have signed an Expression of Intent (EoI) in Jeddah, Saudi Arabia, on 26 October 2026, for a potential Shariah-compliant Line of Financing (LoF) facility of up to USD 10 million, aimed at supporting eligible private sector projects in the Republic of Uzbekistan.

The EoI sets out the intent to establish a Shariah-compliant LoF facility of up to USD 10 million from ICD to Open Bank to be deployed for the onward financing of eligible private sector projects, including small and medium-sized enterprises (SMEs) and corporates operating in the Republic of Uzbekistan. The facility is designed to ensure that financing reaches productive segments of the economy in a manner consistent with Shariah principles and in line with the development objectives of ICD and Uzbekistan.

The intended facility reflects ICD’s commitment to expanding access to Shariah-compliant financial services in Central Asia. By working through Open Bank, a digitally oriented institution with a focus on retail and SME customers, the proposed LoF aims to direct resources toward businesses that can generate meaningful employment opportunities and contribute to sustainable economic growth in Uzbekistan. SME support of this nature plays an important role in strengthening the private sector and broadening economic participation across the country.

ICD’s development mandate centers on advancing private sector growth and improving livelihoods in its member countries through Shariah-compliant financing solutions. The intended LoF with Open Bank aims to contribute to job creation and SME support in Uzbekistan, outcomes that align with ICD’s broader objective of fostering inclusive and sustainable economic development across the IsDB Group’s member countries.

Distributed by APO Group on behalf of Islamic Corporation for the Development of the Private Sector (ICD).


Continue Reading

Trending